Palo Alto でCLIで設定するとき、設定コマンドをset形式で確認したいことがあります。
例えば、現在の設定を確認したり、既存の設定を別のPalo Altoへ移行したりする場合です。
Palo AltoのCLIでは、デフォルトのxml形式の設定表示とは別に、configを以下のようなset形式で表示できます。
set deviceconfig system timezone Japan
set deviceconfig system update-server updates.paloaltonetworks.com
set address address-01 ip-netmask 192.168.1.10/32今回は、Palo Altoのconfigをset形式で取得する方法をまとめてみました。
1.set形式でconfigを確認する
取得は CLI にて行います。
試してみましたが、webコンソールからは set形式で出力ができないようです。
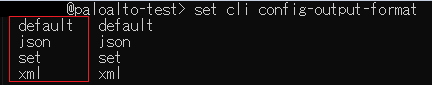
1-1. オペレーショナルモードで以下のコマンドを実行し、出力形式を変更
set cli config-output-format setちなみに「set cli config-output-format」の他の選択肢としては「json」があります
1-2. ページング機能を無効化
set cli pager offconfigの行数はほとんどの場合、CLIの表示行数を超える行数となるのでページング機能が働きます。
最終行までスクロールするのは時間がかかるため、私はよく無効化にしています。
ちなみにページング機能が働いた場合には「Shift + Q」で抜けることが可能です。
1-3. コンフィグレーションモードに入り「show」を実行
実行すると以下のようにset形式のcofnigが表示されます。
xxxxxx@paloalto-test# show
set deviceconfig system type dhcp-client send-hostname yes
set deviceconfig system type dhcp-client send-client-id no
set deviceconfig system type dhcp-client accept-dhcp-hostname no
set deviceconfig system type dhcp-client accept-dhcp-domain no
set deviceconfig system update-server updates.paloaltonetworks.com
set deviceconfig system update-schedule threats recurring weekly day-of-week wednesday
set deviceconfig system update-schedule threats recurring weekly at 01:02
set deviceconfig system update-schedule threats recurring weekly action download-only
set deviceconfig system timezone Japan

 ~~中略~~

set address-group address-group-01 static address-02
set address address-01 ip-netmask 11.11.11.11/32
set address address-01 tag tag1
set address address-02 ip-netmask 11.11.11.12/32
set address address-02 tag tag1
set mgt-config users xxxxxx phash xxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxx
set mgt-config users xxxxxx permissions role-based superuser yes
set mgt-config password-complexity enabled yes
set mgt-config password-complexity minimum-length 8
[edit]
xxxxxx@paloalto-test#
ここで表示された set形式のコマンドはそのまま CLIコマンドとして palaolto に設定が可能です。
CLIコマンドを利用した設定方法については以下の記事にもまとめていますので参考にしてください。
2.特定の設定だけをset形式で取得する
「show」コマンドを実行するとすべてのconfigが取得できますが、例えばセキュリティポリシーの設定だけを取り出したいなど、特定の設定値だけを取り出したい場合もあるかと思います。
そのときには「match」を利用することで特定の設定値のみを取得することが可能です。
「match」は Linux の [grep] のコマンドと同じように「|」の後に記載します。
以下では例としてセキュリティポリシーだけを set形式で抜き出します。
show | match 'rulebase security rules'以下のような出力となり、セキュリティポリシーの設定だけを抜き出すことができます。
xxxxxx@paloalto-test# show | match 'rulebase security rules'
set rulebase security rules Allow-01 to Untrust
set rulebase security rules Allow-01 from Trust
set rulebase security rules Allow-01 source any
set rulebase security rules Allow-01 destination any
set rulebase security rules Allow-01 source-user any
set rulebase security rules Allow-01 category URL-yahoo
set rulebase security rules Allow-01 application any
set rulebase security rules Allow-01 service any
set rulebase security rules Allow-01 source-hip any
set rulebase security rules Allow-01 destination-hip any
set rulebase security rules Allow-01 action allow
set rulebase security rules Allow-01 log-start no
set rulebase security rules All-Deny to any
set rulebase security rules All-Deny from any
set rulebase security rules All-Deny source any
set rulebase security rules All-Deny destination any
set rulebase security rules All-Deny source-user any
set rulebase security rules All-Deny category any
set rulebase security rules All-Deny application any
set rulebase security rules All-Deny service any
set rulebase security rules All-Deny source-hip any
set rulebase security rules All-Deny destination-hip any
set rulebase security rules All-Deny action deny
[edit]
xxxxxx@paloalto-test#
ただし、デフォルトで設定されているポリシーについては出力されないので、その部分は覚えておいてください。
4. よく使うset形式の確認方法
以下のようなコマンドを覚えておくと便利です。
Security Policy
show | match 'rulebase security rules'NAT Policy
show | match 'rulebase nat rules'Address
show | match '^set address 'Address Group
show | match '^set address-group 'Service
show | match '^set service 'Interface
show | match 'network interface'設定項目が多い場合は、match を使って必要な部分だけ取り出すと確認しやすくなります。
5.set形式から元のconfigを確認するときの注意点
set形式で表示される設定はとても便利ですが、表示された内容をそのまま別の環境へ投入できるとは限りません。
例えば、以下のような設定等が移行先の環境と一致している必要があります。
- インターフェース名
- IPアドレス
- Zone
- Virtual Router
- VSYS
- オブジェクト名
- 参照しているPolicy
- Panorama管理下の設定
特に、既存環境の設定を別のPalo Altoへ移行する場合は、設定をそのままコピーするのではなく、依存関係を確認してから投入することが必要になります。
6.まとめ
今回は、Palo Altoのconfigを set形式で取得する方法をまとめました。
基本的な手順は以下の3ステップです。
① 出力形式をsetに変更
set cli config-output-format set② Configuration modeへ移動
configure③ configを表示
showこれだけで、Palo Altoのconfigをset形式で確認できます。
また、特定の設定だけ確認したい場合は、match を利用することで確認できます。
show | match 'rulebase security rules'Palo Altoの設定をCLIで確認・編集したり、別のファイアウォールへ移行したりするときは、set形式でconfigを取得しておくと作業しやすくなります。